
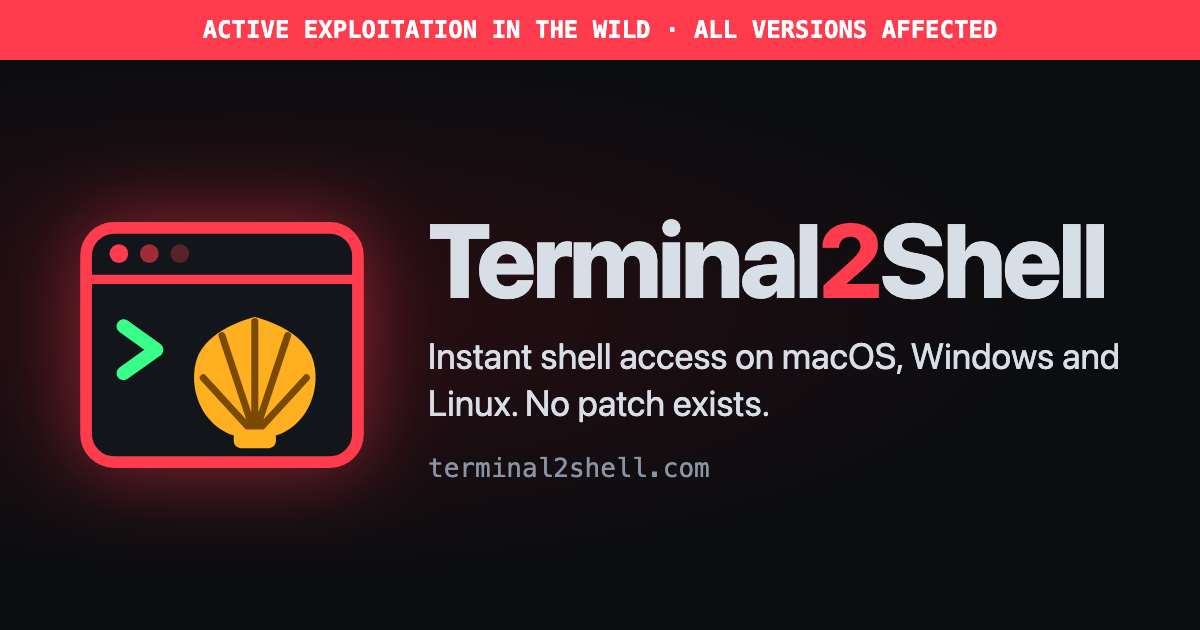
Saw this scrolling All, took me a sec (it’s early am). Just about shat meself, i just finished fucking patching 350 deb boxes for the goddamn PHP cve and CA debacles
This may have caused some unwarranted heart attacks lol
Have you seen what happens why you hit
F12in a browser?Thanks, I changed my bank account to have 100 million dollars with that one weird trick.
Don’t even joke, I would not be surprised if our security team latched onto this unironically.
That’s kind of the point. Security teams have stopped doing any risk assessment after Heartbleed, and now all it takes is a pretty website to have a “real” vulnerability
Jokes on you, my server has no terminal, not even a shell (I use Talos, everything is managed via mTLS protected API)

Fuck that’s a lot of critical infrastructure that’s vulnerable!
Type slower! That made me laugh
Got me for a second! 😅
Me using HaikuOS and AmigaOS: ha suck it!
Amigaos has a shell, joke’s on you.
Dear God… nobody is safe :O
This does however make me wonder if it’s possible to interact with a Linux system without first logging in. Some bootloaders have a shell and I think there’s also a UEFI shell? No idea what they are capable of, though.
Not directly. UEFI itself only supports mounting a minimal set of filesystems. That’s why your EFI system partitiion needs to be FAT32, for example, and why the kernel and initial ramdisk are also located there. UEFI mounts the ESP and executes the bootloader, which then loads the kernel (located at
ESP/vmlinuz-linuxon Arch) and initial ramdisk (ESP/initramfs-linux.img) into memory. The initial ramdisk is a compressed image of an early root filesystem that contains the tools and drivers necessary to boot the full system, including the filesystem drivers for ext4/btrfs/whatever.You could build an EFI program that natively supports different filesystems, though.
I mean you can easily edit grub at boot and boot straight into single user mode without logging in.