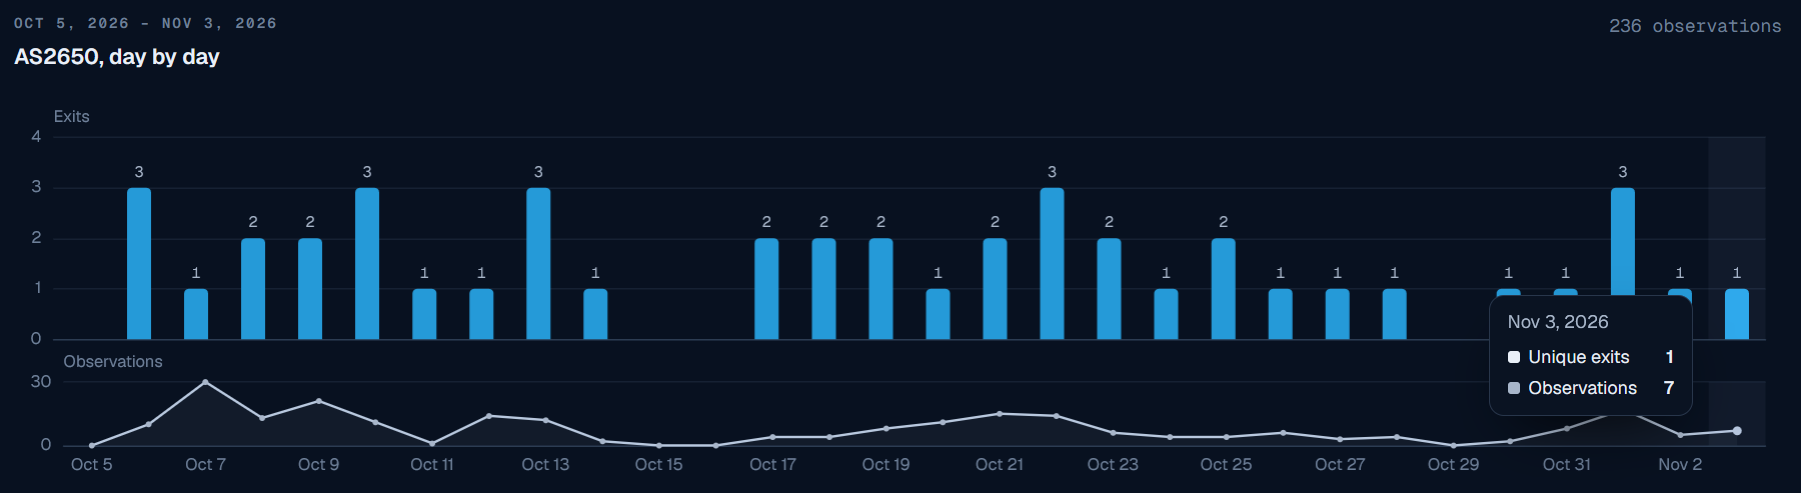
Our new Residential Proxy Observatory shows residential proxy traffic exiting the White House network: 236 times in 30 days, through 28 public proxy services.
Dodgy app developers make dodgy apps, and convince naive users to install them.
The dodgy apps make the naive user’s Internet connection available to some partner the dodgy app developer has done a deal with - and since the naive user is typically using a residential network, and it lets their connection be used by someone else, it’s called a residential proxy.
The partner sells access to a huge network of residential proxies to scrapers, often those wanting to do AI scraping against the wishes of the owners of the site being scraped. This is valuable to the scrapers because they appear to be coming from large numbers of different residential addresses. Cloud / hosting provider addresses are usually the first thing people block if they don’t want scrapers, and they also block how much each address can access. So the scrapers scrape a little bit per address, making it hard for the victim sites to detect what is scraping and what is legitimate traffic.
This creates a security risk for the naive users, because as well as connecting out to the Internet, usually the proxy customer can connect to and maybe exploit things on their home network. The naive users usually don’t know their connection is being used this way.
So the headline here is that one of the affected naive users is someone in the White House, and one of the ‘residential’ networks being sold is in fact the White House’s Internet connection.
So, like, here I am, on my phone, playing games and browsing the internet. Sometimes my connection is a little slow, but that’s just the nature of things because sometimes it just takes a tiny bit longer to get a response and sometimes my phone just runs a little slow.
What I don’t know is that my phone is infected with malware. And that malware lets other people access whatever internet I have access to; and that whatever those other people are doing looks like it’s coming from my IP address and my device. I am the unwitting exit node for an unscrupulous VPN service (or driving similar).
Someone working in the White House has an infected phone and doesn’t know it. They are at the White House most days, work late afternoon to around midnight.
If the person in charge of the botnet knew the phone of a White House worked was compromised, they could use that access to appear as a legitimate user and bypass security protocols, have accounts and passwords compromised, and have their data scraped and stolen.
I would assume most normal people working in the White House have their phones regularly checked for malware, or use special phones for government work. However, higher ups in the Trump White House have routinely violated and ignored security protocols; they could abuse their power to use their own personal phones and to ignore security checks.
Given that the times the node was used are so consistent, I think it’s unlikely that there are two infected phones involved.
Given that this happened on most days in October, it’s unlikely to be Trump or anyone who regularly travels with him, because he spends a lot of time not at the White House. There was no exit node activity on two Thursdays, one Friday and one Monday; activity was recorded every other day in October. Meaning this isn’t someone who comes into the office M-F with weekends off; days off seem to be somewhat rare for this person, and don’t occur on normal weekends. I have no idea who the person is, but security should probably make more of an effort to re-secure all phones permitted on the premises.
However, higher ups in the Trump White House have routinely violated and ignored security protocols; they could abuse their power to use their own personal phones and to ignore security checks.
They’re so dumb that they probably just hired the hacker so hacking could be unnecessary.

I read through this whole article and still don’t really understand it. Can anyone ELI5?
Dodgy app developers make dodgy apps, and convince naive users to install them.
The dodgy apps make the naive user’s Internet connection available to some partner the dodgy app developer has done a deal with - and since the naive user is typically using a residential network, and it lets their connection be used by someone else, it’s called a residential proxy.
The partner sells access to a huge network of residential proxies to scrapers, often those wanting to do AI scraping against the wishes of the owners of the site being scraped. This is valuable to the scrapers because they appear to be coming from large numbers of different residential addresses. Cloud / hosting provider addresses are usually the first thing people block if they don’t want scrapers, and they also block how much each address can access. So the scrapers scrape a little bit per address, making it hard for the victim sites to detect what is scraping and what is legitimate traffic.
This creates a security risk for the naive users, because as well as connecting out to the Internet, usually the proxy customer can connect to and maybe exploit things on their home network. The naive users usually don’t know their connection is being used this way.
So the headline here is that one of the affected naive users is someone in the White House, and one of the ‘residential’ networks being sold is in fact the White House’s Internet connection.
Many thanks!
So, like, here I am, on my phone, playing games and browsing the internet. Sometimes my connection is a little slow, but that’s just the nature of things because sometimes it just takes a tiny bit longer to get a response and sometimes my phone just runs a little slow.
What I don’t know is that my phone is infected with malware. And that malware lets other people access whatever internet I have access to; and that whatever those other people are doing looks like it’s coming from my IP address and my device. I am the unwitting exit node for an unscrupulous VPN service (or driving similar).
Someone working in the White House has an infected phone and doesn’t know it. They are at the White House most days, work late afternoon to around midnight.
If the person in charge of the botnet knew the phone of a White House worked was compromised, they could use that access to appear as a legitimate user and bypass security protocols, have accounts and passwords compromised, and have their data scraped and stolen.
I would assume most normal people working in the White House have their phones regularly checked for malware, or use special phones for government work. However, higher ups in the Trump White House have routinely violated and ignored security protocols; they could abuse their power to use their own personal phones and to ignore security checks.
Given that the times the node was used are so consistent, I think it’s unlikely that there are two infected phones involved.
Given that this happened on most days in October, it’s unlikely to be Trump or anyone who regularly travels with him, because he spends a lot of time not at the White House. There was no exit node activity on two Thursdays, one Friday and one Monday; activity was recorded every other day in October. Meaning this isn’t someone who comes into the office M-F with weekends off; days off seem to be somewhat rare for this person, and don’t occur on normal weekends. I have no idea who the person is, but security should probably make more of an effort to re-secure all phones permitted on the premises.
They’re so dumb that they probably just hired the hacker so hacking could be unnecessary.
Thanks for that!